
Consent Management Systems in 2026: 7 Checks Before You Trust the Stack
Teams researching consent management systems usually do not need another generic privacy article. They need a practical read on how the controls behave on a live build, where the friction shows up, and what should be tested before a site ships.
For adjacent context, start with the linked DataShyre guides, then validate the controls on a live build so implementation gaps show up before release.
If you want nearby context first, start with these guides to consent management platform, consent management process, and consent management tooling. This page is narrower. It is the seven-check review I would use this week before trusting consent management systems on a live site.
1. Start with collection points, not the banner
The first mistake with consent management systems is treating consent as a user-interface problem.
In real deployments, the system has to govern every place where storage, access, or downstream sharing can happen. The European Commission’s consent guidance still requires specific purposes, a clear affirmative act, and requests written in “clear and plain language.” The ICO’s final storage-and-access-technologies guidance, published on April 29, 2026, also makes clear that the operational scope is broader than classic cookies. It covers cookies, tracking pixels, device fingerprinting, scripts, and similar technologies.
So the first check is simple: can your team name every tag, SDK, embed, plugin, pixel, and script the system is meant to control? If not, the banner is already ahead of the governance.
2. Check whether the regional logic matches the law you say it supports
Weak consent management systems often collapse every market into one flow.
That is risky because the legal trigger is not identical everywhere. For EU-facing consent flows, the Commission still says consent must be freely given, informed, specific, and tied to a real affirmative act. The same guidance also says withdrawal must be possible in a way that is “as easy to use as giving consent.” In California, the official focus may shift toward opt-out rights where sale or sharing is in scope, and the California DOJ still describes Global Privacy Control as a “stop selling or sharing my data switch.”
A serious review should therefore test whether the system can:
- branch by geography or applicable rule set;
- keep optional technologies off until valid prior consent exists where required;
- honor opt-out and GPC logic where California sale or sharing rules apply; and
- keep those branches consistent with the site’s privacy notice and controls.
3. Make purpose mapping and categories explicit
The hardest part of consent management systems is often the middle layer between the banner and the code.
This is where vague categories create false confidence. Analytics, marketing, preferences, functional, and necessary do not enforce themselves. Someone still has to decide which technologies belong where, which purposes they support, and which downstream actions should remain blocked or allowed.
The European Commission’s current materials still tie valid consent to specific purposes. That makes category discipline a live compliance issue, not a labeling exercise. If a system says analytics but one vendor also performs ad measurement or audience sharing, the category map needs to reflect that reality.
In other words, good consent management systems do not only collect a yes or no. They map that choice to precise technical and policy outcomes.
4. Treat runtime enforcement as the product
This is where many consent management systems look complete in admin screenshots and break in production.
Google’s current consent-mode setup guidance says default consent states should be set before any commands that send measurement data, and its debugging guidance says the default state must be in place before any tags or other code use or update consent. For Tag Manager, Google specifically recommends consent-state handling that fires at the right stage rather than trying to catch up later.
That makes runtime behavior the core product:
- denied defaults should land before optional Google measurement runs;
- accept should update the relevant signals cleanly;
- reject should keep them denied;
- non-Google tags and embeds should obey the same choice; and
- later page views or route changes should preserve the same state.
If the interface says Reject all while the network trace still shows optional requests firing first, the system is not trustworthy yet.
5. Make refusal and withdrawal genuinely usable
Good consent management systems do not end at first-layer capture.
The Commission’s guidance still treats easy withdrawal as part of valid consent. CNIL’s current enforcement position is equally useful as a design test: rejecting cookies should be just as easy as accepting them, and banner information should stay clear and complete. California’s CPPA has framed the same problem from the dark-pattern angle, stressing that privacy choices should be symmetrical and that “Dark patterns aren’t about intent, they’re about effect.”
So the system should let you verify that:
- refusal is visible and not demoted into a maze;
- withdrawal stays available after the banner closes;
- preference centers reflect the current state accurately; and
- downstream behavior actually changes after a withdrawal or opt-out.
That is one of the quickest ways to separate decorative banners from real consent management systems.
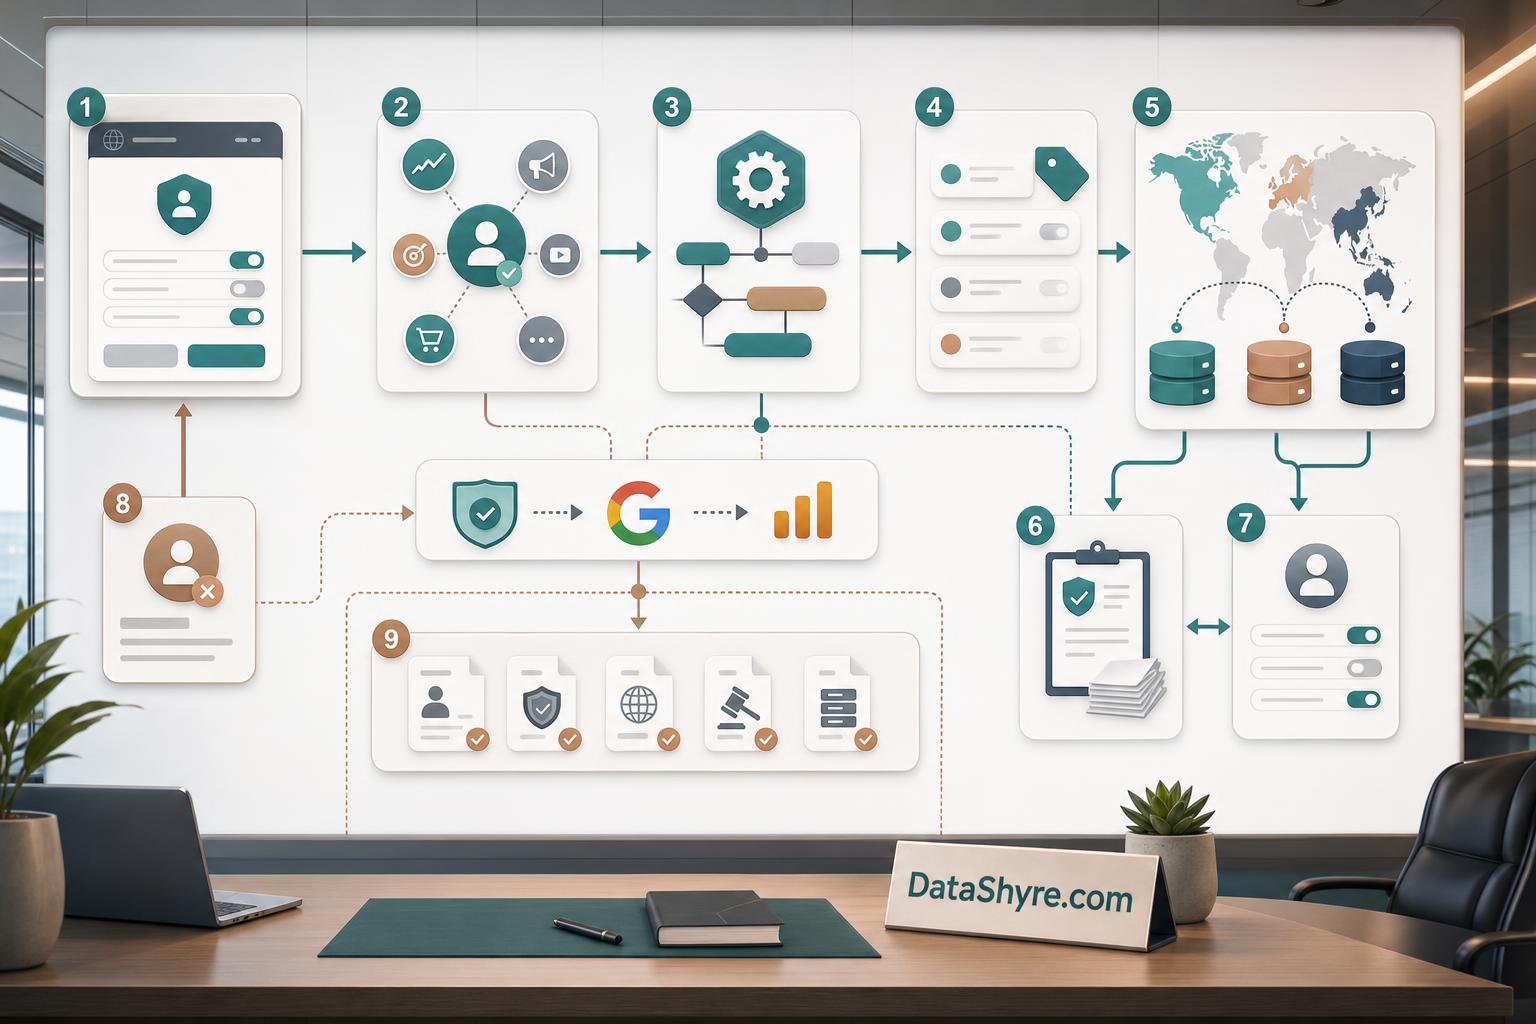
6. Keep records that reconstruct what actually happened
Consent without proof ages badly.
For consent management systems, the record should usually let you reconstruct:
- which interface or banner version was shown;
- which purposes or categories were available;
- what the user chose and when;
- which technical state that choice produced; and
- whether a later withdrawal, opt-out, or rule change occurred.
This matters because logs and runtime behavior can drift apart. A database value that says rejected is weak evidence if the browser trace or vendor console shows optional measurement still firing.
7. Re-test after every meaningful change
The best consent management systems are not static compliance artifacts. They are release-sensitive operating controls.
The ICO’s current storage-and-access-technologies guidance asks practical questions about whether you are using the same technology for multiple purposes and what happens when technologies or purposes change. That is the operational reason retesting matters. New scripts, tag-manager changes, site redesigns, vendor updates, new embeds, and revised region settings can all make yesterday’s configuration untrue.
So if I were operating consent management systems in 2026, I would treat these as automatic retest triggers:
- a new tag, SDK, or vendor;
- a banner or preference-center redesign;
- a GTM or script-order change;
- a new region or rule branch;
- a policy or category-mapping change.
A short live review sequence for this week
If I were pressure-testing consent management systems on a live property today, I would work in this order:
- inventory every technology the system is supposed to govern;
- test the regional branches separately;
- review the purpose map and category assignments;
- inspect first-load runtime behavior before any choice;
- test refusal, acceptance, and later withdrawal;
- compare stored records with browser behavior;
- repeat after the latest release or vendor change.
That sequence usually reveals more truth than another round of vendor-demo screenshots.
Bottom line
The cleanest way to think about consent management systems in 2026 is this: the product is not the banner. The product is the chain from user choice to technical enforcement to audit proof.
The practical test for consent management systems is simple: if the site can explain the rule, enforce the choice, and keep that behavior stable through ordinary releases, the setup is moving in the right direction.
Sources
- European Commission: Legal grounds for processing data
- UK ICO: Final storage and access technologies guidance published
- UK ICO: Guidance on the use of storage and access technologies
- CNIL: Dark Patterns in Cookie Banners: CNIL issues formal notice to website publishers
- California DOJ: California Consumer Privacy Act
- California DOJ: Global Privacy Control
- CPPA: Enforcement Advisory Stresses the Importance of Avoiding Dark Patterns
- Google for Developers: Set up consent mode on websites
- Google for Developers: Troubleshoot consent mode with Tag Assistant
—
Published: October 16, 2026. Updated using current official European Commission, ICO, CNIL, California DOJ, CPPA, and Google materials available at publication time.