
Consumer Consent Management in 2026: 7 Checks Before You Trust the Workflow
Teams researching consumer consent management usually do not need another generic privacy article. They need a practical read on how the controls behave on a live build, where the friction shows up, and what should be tested before a site ships.
For adjacent context, start with the linked DataShyre guides, then validate the controls on a live build so implementation gaps show up before release.
This is why the current official baseline matters. The European Commission still says a consent request should use “clear and plain language.” The UK’s ICO finalized its storage-and-access-technologies guidance on April 29, 2026 and says a consent mechanism must “function as intended.” California’s Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch.” And Google’s current consent-mode guide still tells implementers to set defaults “before any commands that send measurement data.”
If you want the closest companion reads first, start with these guides to consent management platform, consent preferences, and CCPA consent requirements. This article stays broader. It is the seven-check review I would use this week before trusting any consumer consent management workflow on a live site or app.
What consumer consent management actually covers
Good consumer consent management is not one screen. It is the chain that connects a person’s choice to real behavior across:
- website banners and preference centers;
- mobile app permission or privacy settings;
- analytics, advertising, and personalization tools;
- browser-based privacy signals such as GPC;
- CRM, CDP, email, or SMS suppression logic;
- records showing what the person saw, chose, and changed later.
This is why teams get into trouble when they evaluate consent only at the interface layer. The banner can look balanced while a tag fires too early, an app SDK ignores the user’s later change, or an account preference never reaches downstream messaging systems.
1. Separate consent, opt-out, and preference logic by jurisdiction
The first mistake in consumer consent management is treating every privacy choice as the same legal event.
In the EU and UK, the live question often starts with whether non-essential storage, access, or related processing waits for valid consent. The European Commission’s consent guidance still frames the basics around free choice, specific information, and a clear affirmative act. The ICO’s current storage-and-access guidance broadens the operational scope beyond old cookie-only language into pixels, fingerprinting, scripts, and similar technologies.
California often begins from a different place. The CPPA’s current FAQs still say consumers may opt out of sale or sharing, including through qualifying opt-out preference signals such as GPC, and that businesses cannot resume sale or sharing after that request unless the consumer later consents. The CCPA regulations effective January 1, 2026 also remain part of the current operating baseline.
So a real consumer consent management design has to answer separate questions:
- where prior consent is required before optional tracking or profiling begins;
- where opt-out rights or limit rights control the flow instead;
- where minors, sensitive data, or channel-specific rules create additional conditions.
One generic global toggle is usually too blunt.
2. Ask by purpose and channel, not in one convenient bundle
This is where many systems become hard to defend.
The Commission still says people should be told all the reasons for processing in clear terms. The ICO’s consent guidance says requests should be specific to purpose and usually require granular options. In real deployments, that means a strong consumer consent management flow distinguishes what the user is agreeing to instead of rolling unlike activities into one yes.
On a live review, I would usually test whether the system separates:
- analytics or measurement;
- advertising or remarketing;
- personalization;
- embedded-media or social features that bring optional tracking;
- marketing communications such as email or SMS where those are managed in the same preference layer.
This also applies across channels. A user may be willing to receive product emails but not targeted advertising, or may allow basic analytics while rejecting cross-context behavioral advertising. Bundled language makes those differences disappear even when the law or the customer expectation does not.
3. Make the choice change behavior before optional data use starts
This is still the most practical test.
The ICO’s current guidance says you must not pre-enable non-exempt storage and access technologies and that the mechanism must “function as intended.” Google’s consent-mode documentation adds a useful implementation signal for web teams: default states should be set “before any commands that send measurement data.”
That makes consumer consent management partly a timing review:
- what runs on first page load or first app open;
- what runs only after the user accepts;
- what remains off after the user rejects;
- what changes later if the user withdraws or updates preferences.
Common failures are still predictable:
- a tag manager loads optional tools before defaults are set;
- an embedded player or chat widget sets identifiers on render;
- mobile SDKs initialize before the preference state is applied;
- one system honors the choice while another keeps sending data anyway.
If the interface says one thing and the runtime trace says another, trust the trace.
4. Keep refusal and withdrawal just as usable as acceptance
This is not only design polish. It is validity.
The European Commission still says withdrawing consent should be as easy as giving it. CNIL’s formal notices on misleading cookie banners still say rejecting cookies should be just as easy as accepting them. The ICO’s examples now show the same practical standard with equal prominence for Accept all and Reject all where consent is the basis.
For consumer consent management, that means checking whether:
- refusal is available on the first meaningful layer where it should be;
- later withdrawal is visible and not hidden in a legal maze;
- the saved preference center reflects the current state accurately;
- changing the choice later actually changes live behavior.
This is where a lot of systems become decorative. The first prompt works. The later controls do not.
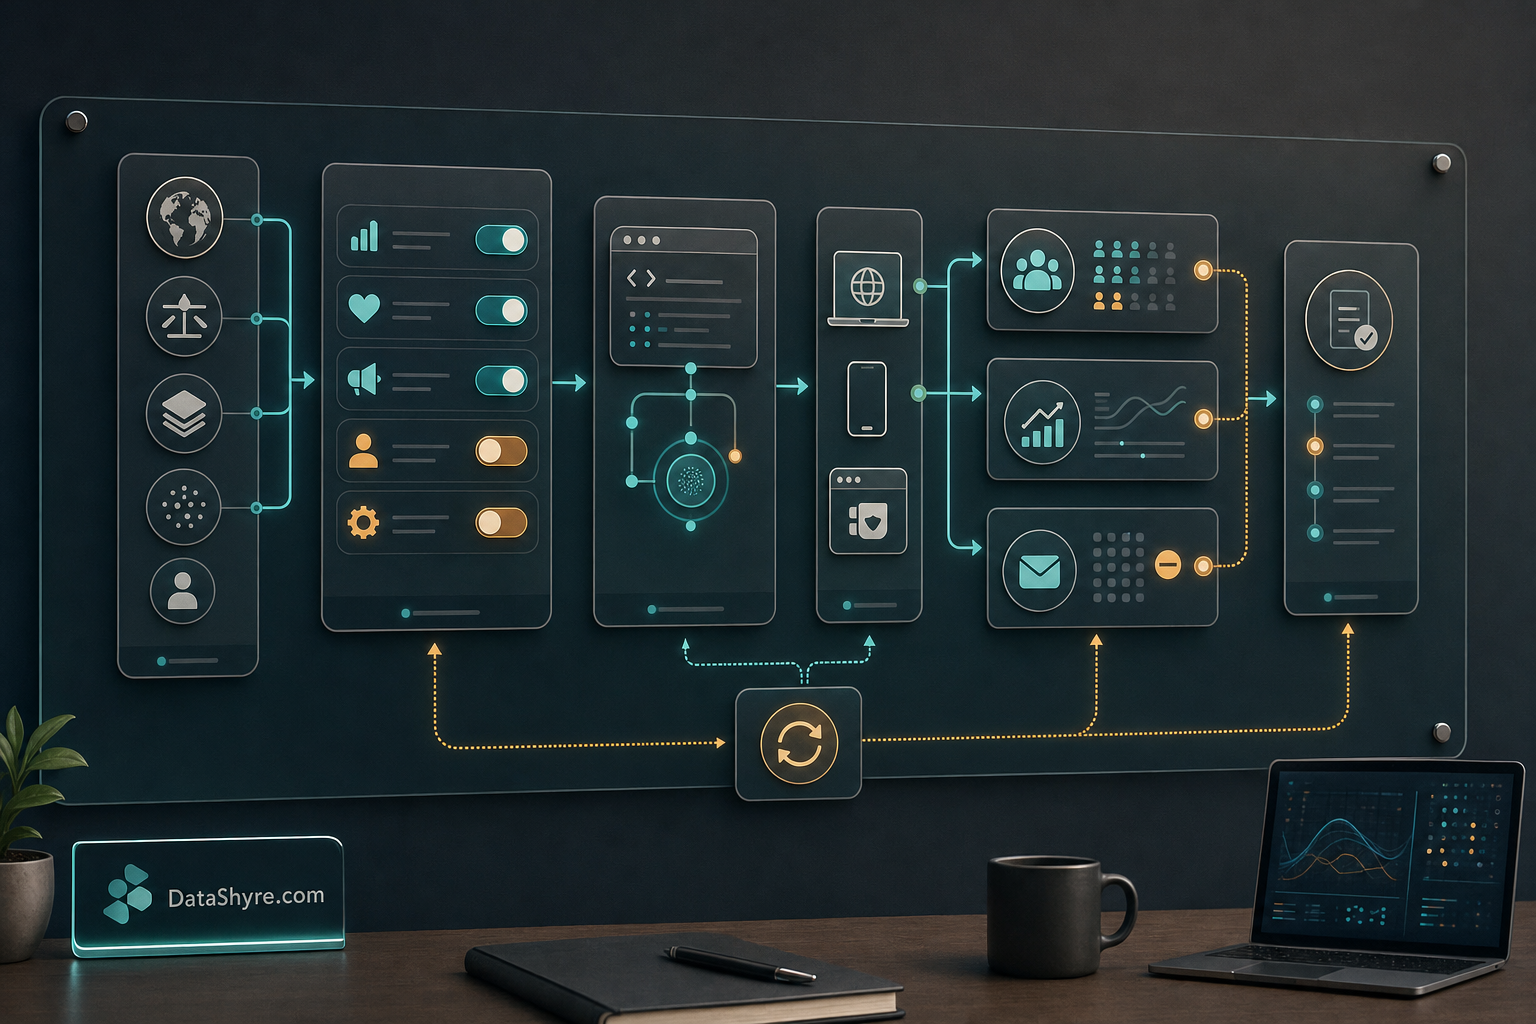
5. Honor browser and account-level signals across systems
Modern consumer consent management breaks when the business records a preference in one place but ignores it somewhere else.
California remains the clearest example. The DOJ still describes GPC as a “stop selling or sharing my data switch.” The CPPA FAQ still says businesses must honor qualifying opt-out preference signals and, in most instances, also provide a clear on-site link such as Your Privacy Choices or Do Not Sell or Share My Personal Information when those rights apply.
That means you should test more than the banner:
- does GPC change sale-or-sharing behavior on first visit;
- does the account preference center reflect or complement the browser signal correctly;
- do email, ad, analytics, and downstream identity systems receive the right suppression state;
- does the same logic hold across web, app, and connected services.
This is one of the clearest lines between a preference capture tool and real consumer consent management.
6. Keep records a real team can explain later
Consent and preference systems are often trusted until someone asks for proof.
The ICO’s guidance says service providers must be able to demonstrate that someone provided consent and notes that CMPs are often used to keep those records. For consumer consent management, usable proof usually means more than a binary yes-or-no flag.
I would expect the system to preserve:
- what the person saw;
- when they acted;
- which purpose-level settings they chose;
- which policy or interface version was live;
- what changed after withdrawal or later updates;
- which systems were supposed to receive the signal.
If your team cannot reconstruct that story without guesswork, the records are thinner than they look.
7. Re-test after releases, vendor changes, and new channels
This is the part teams underfund.
Consumer data flows change constantly. Marketing adds a new tool. Product changes an onboarding screen. Engineering adjusts script order. Mobile teams release a new SDK version. Privacy notices are updated without checking whether the actual enforcement path changed with them.
The ICO’s guidance explicitly points teams toward regular reviews, and its consent examples are clear that new purposes or new third parties can require fresh consent. So for consumer consent management, I would treat these as automatic re-test triggers:
- new tags, SDKs, or embedded services;
- new ad-tech or analytics vendors;
- updated preference-center copy or category structure;
- new regions, brands, or language flows;
- app, website, or identity-layer releases that can change timing or signal propagation.
A privacy workflow that only passed once is not yet operational.
A short operating standard for 2026
If I had to reduce consumer consent management to one working standard in late 2026, it would be this:
- ask in clear purpose-specific terms;
- apply the right legal model by region and channel;
- keep optional data use off until the right condition exists;
- make refusal and withdrawal genuinely usable;
- honor browser, account, and downstream signals consistently;
- keep proof your team can still explain after the stack changes.
That is a much better definition than “has a banner.”
Bottom line
Consumer consent management in 2026 is the control layer that turns privacy choice into live system behavior.
The practical test for consumer consent management is simple: if the site can explain the rule, enforce the choice, and keep that behavior stable through ordinary releases, the setup is moving in the right direction.
Sources
- European Commission: When is consent valid?
- European Commission: Information for individuals
- ICO: Final storage and access technologies guidance published
- ICO: How do we comply with the PECR rules?
- ICO: How do we manage consent in practice?
- CNIL: Dark Patterns in Cookie Banners
- California DOJ: Global Privacy Control
- California Privacy Protection Agency: FAQs
- California Privacy Protection Agency: Law & Regulations
- California Privacy Protection Agency: CCPA Updates effective January 1, 2026
- Google for Developers: Set up consent mode on websites
—
Published: October 16, 2026. Updated using current official regulator, government, and platform materials available at publication time.